Supplier cyber risk on capital projects: NIS2, the EU Cyber Resilience Act from 11 September 2026, IEC 62443 and the OT vendor access a new plant inherits.
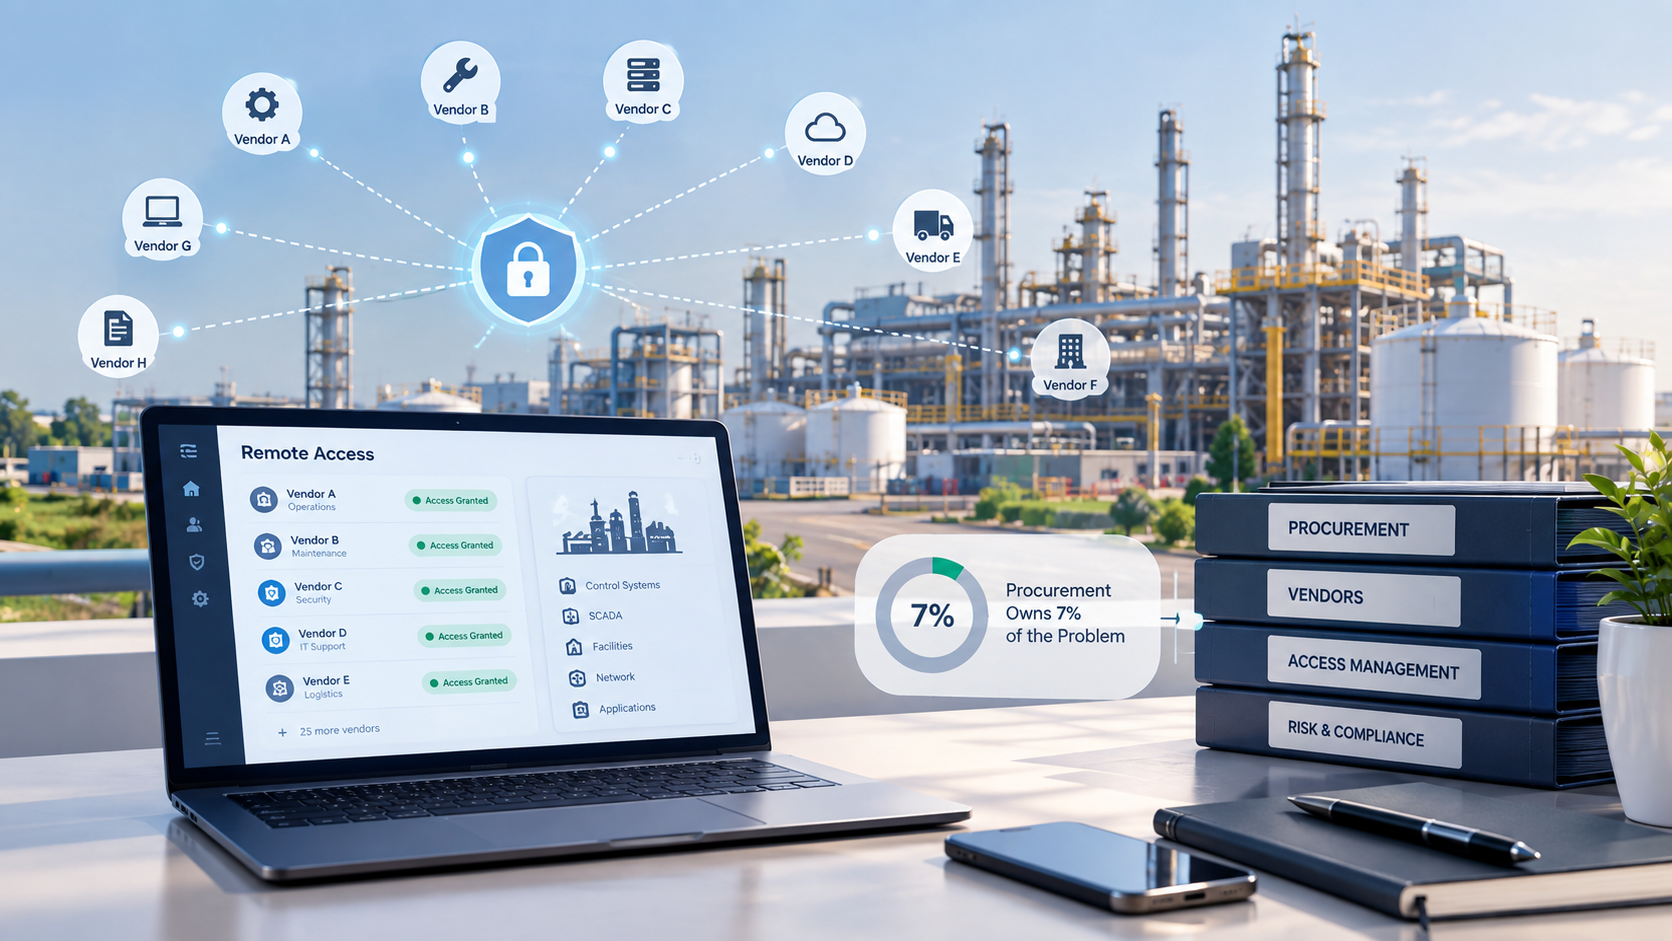
A refinery, LNG train or concentrator that starts up in 2029 does not arrive with one supplier. It arrives with a control system vendor, an instrumentation vendor, three or four analyzer suppliers, a rotating-equipment OEM with condition-monitoring telemetry, a fire-and-gas package supplier, a systems integrator, and a maintenance contractor – most of them holding, on day one of operations, a standing remote connection into the process network that was opened during commissioning and never closed.
The Ponemon Institute, surveying 1,056 security professionals across manufacturing, energy and oil and gas, found that 73% of industrial organisations allow vendors and other third parties access to the OT environment, at an average of 77 authorised third parties per organisation. Sixty percent had authorised more than 50; 25% had authorised more than 100. In the same study, only 27% maintained an accurate OT asset inventory.
That population is assembled during a capital project, by procurement, package by package. It is almost never specified as a security decision, and it is very rarely handed over as a managed list.
The evidence that this is now the dominant intrusion route
The 2026 Verizon Data Breach Investigations Report, published 19 May 2026 and covering more than 31,000 incidents and 22,000 confirmed breaches from November 2024 to October 2025, found that breaches with third-party involvement rose 60% year on year to 48% of all breaches – the second consecutive sharp rise, following the move from 15% to 30% recorded in the 2025 edition. Verizon’s definition is broader than most readers assume and precisely describes the OT vendor case: a supplier in the software supply chain, a supplier hosting the organization’s data, or a supplier with a connection into the organization’s environment enabling lateral movement.
The manufacturing cut is worse than the economy-wide figure. Across 3,627 incidents and 2,713 confirmed breaches, third-party involvement reached 61%, with vulnerability exploitation the leading initial access vector at 38% and ransomware present in 61% of breaches.
Dragos’s 2026 OT/ICS Year in Review, published 17 February 2026 and covering calendar 2025, adds the operational texture. Across its services engagements, 49% of reports contained elevated findings related to remote access and 81% found poor IT/OT network segmentation. In the oil and gas subset, 73% of incident response cases involved VPN or jumphost credential reuse or exploitation, and default credentials were found in 26% of oil and gas engagements — credentials that, in a plant, are overwhelmingly a commissioning artefact. Every OT ransomware case Dragos handled in 2025 produced significant operational disruption; most incident response cases produced at least a one-week outage.
And the buyers know the control gap exists. Claroty’s 2025 Global State of CPS Security study (n = 1,100, published 17 September 2025) found that 46% had experienced a breach in the preceding twelve months due to third-party access, and – the single most procurement-pointed statistic in this field – that 54% discovered security gaps in their vendor contracts only after an incident. The SANS Institute’s State of ICS/OT Security 2025 (n = 330, published 14 November 2025) found that 31% have no formal centralized inventory of active ICS/OT remote access points, and that vendor-managed and third-party access restrictions are fully implemented across all remote access points by only 32% of respondents.
What changed on 11 September 2026
Until recently this was a risk argument. It is now, for anyone buying equipment onto the EU market, a legal one.
The EU Cyber Resilience Act – Regulation (EU) 2024/2847 – brought Article 14 into application on 11 September 2026. The regulation’s substantive obligations do not apply until 11 December 2027, but the reporting duties are live now. A manufacturer of a product with digital elements must notify any actively exploited vulnerability to the coordinating CSIRT and ENISA within 24 hours as an early warning, with a fuller notification within 72 hours and a final report within 14 days of a fix becoming available. Severe incidents follow the same 24/72-hour clock with a final report one month after notification.
Article 14(8) is the limb that matters to a plant operator: the manufacturer must inform impacted users of the vulnerability or incident and of available mitigations, where appropriate in a structured, machine-readable format — and where it fails to do so in a timely manner, the national CSIRT may tell the users directly.
The scope reaches further than most specifications assume. Article 2(1) covers products whose foreseeable use includes a direct or indirect logical or physical data connection, and Article 3 defines a product with digital elements to include its remote data processing solutions. A PLC, RTU, analyser or vibration-monitoring unit is in scope; so is the vendor’s own condition-monitoring cloud platform where the product cannot function without it.
One nuance worth getting right, because industry commentary routinely gets it wrong: Annexes III and IV of the CRA name no ICS, PLC, DCS or SCADA category. Control hardware sits in the default class, and the manufacturer may self-assess. What is listed as “important” is the plumbing around it – VPN products, privileged access management, network management systems, routers and switches (Class I), and firewalls and intrusion detection and prevention systems (Class II), which under Article 32(3) cannot be self-assessed at all and require a notified body. The regulation bites hardest precisely on the remote-access layer that the vendor population depends on.
The obligation that lands on the buyer
NIS2 – Directive (EU) 2022/2555 – puts the corresponding duty on the operator. Article 21(2)(d) requires supply chain security measures covering “security-related aspects concerning the relationships between each entity and its direct suppliers or service providers.” Article 21(3) is the load-bearing sentence: entities must take into account the vulnerabilities specific to each direct supplier and service provider, the overall quality of their products and cybersecurity practices, and their secure development procedures.
That is a per-vendor evidence file, not a policy document. And Article 20 requires management bodies to approve those measures, oversee implementation, and be capable of being held liable for infringements. Article 34 sets administrative fines for essential entities at a maximum of at least EUR 10 million or 2% of total worldwide annual turnover, whichever is higher; important entities at EUR 7 million or 1.4%.
Two scope points a mining or refinery audience needs stated plainly. Annex I names oil production, refining and treatment facilities, gas refining and treatment facilities, LNG system operators and hydrogen production explicitly – no interpretation required. Mining is not in NIS2 at all, in either annex; a new mine in the EU is out of scope unless a Member State designates it or it falls under the Critical Entities Resilience Directive. And a useful commercial fact: the DCS, instrumentation and analyzer makers themselves fall under Annex II manufacturing (NACE C26, C27, C28) as important entities. The vendor is already regulated. That is leverage in a negotiation, not a favor you are asking for.
As at 8 July 2026 the Commission had referred Ireland, Spain, France and the Netherlands to the Court of Justice for failing to notify full transposition, with a request for lump sum and daily penalties – so the national picture is uneven, but the direction is not in doubt.
Outside Europe, the Gulf is further ahead on the specific question of vendor obligations. Saudi Arabia’s National Cybersecurity Authority Operational Technology Cybersecurity Controls (OTCC-1:2022), backed by royal decree and applying to critical facilities including those owned abroad, devotes an entire domain to third-party cybersecurity: control 4-1-1-1 requires cybersecurity requirements to be included during the procurement lifecycle; 4-1-1-3 requires third-party contractors and vendors to use formal, documented secure development lifecycle practices; 4-1-1-4 requires periodic cybersecurity assessment and audit of third-party providers. The companion ECC-2:2024 goes further on remote support: managed service centres using remote access must be fully located in the Kingdom, which is a live constraint on any European or US vendor proposing to monitor a Saudi plant from an overseas operations centre.
In the US, the picture is directives rather than rules. CIRCIA’s final rule has slipped past its statutory deadline with no compliance date; the TSA surface cyber risk management rule sits in “Long-Term Actions”. But FERC Order No. 912, issued 18 September 2025, formally found the existing NERC supply chain standards insufficient and directed replacements within 18 months. CIP-013-2 already requires procurement processes covering vendor notification when remote or onsite access should no longer be granted to vendor representatives, and coordination of controls for vendor-initiated remote access – while expressly carving out contract terms and vendor performance from its scope. That carve-out is the gap Order 912 is closing.
Where this has to be fixed: the specification, not the handover
The most useful dataset on this question is also the newest. Black & Veatch and Takepoint Research surveyed 451 owners, operators, engineering leaders and EPC stakeholders, publishing in April 2026. The findings:
- 72% say OT cybersecurity enters industrial capital projects late or not at all. Only 24% say it is always or often included early.
- Asked who owns it: EPCs 29%, owner IT and corporate security 28%, owner OT engineering 22%, procurement 7%, shared 4%, no clear owner 10%.
- 68% cite unclear ownership as a core breakdown. Only 8% describe EPC and asset-owner alignment on OT cybersecurity as very strong; 57% describe it as poor or non-existent.
- 76% want cybersecurity embedded directly into specifications, and 68% want contract and specification templates to do it.
That last pair is the resolution. There are three clauses that belong in a capital project specification and the third is the one usually missing:
- IEC 62443-4-1 on the product manufacturer – does the DCS or PLC vendor run a documented secure development lifecycle?
- IEC 62443-4-2 on the product – the component security capability level, stated as the seven-element vector across the foundational requirements, per zone. “SL3” on its own is not a specification.
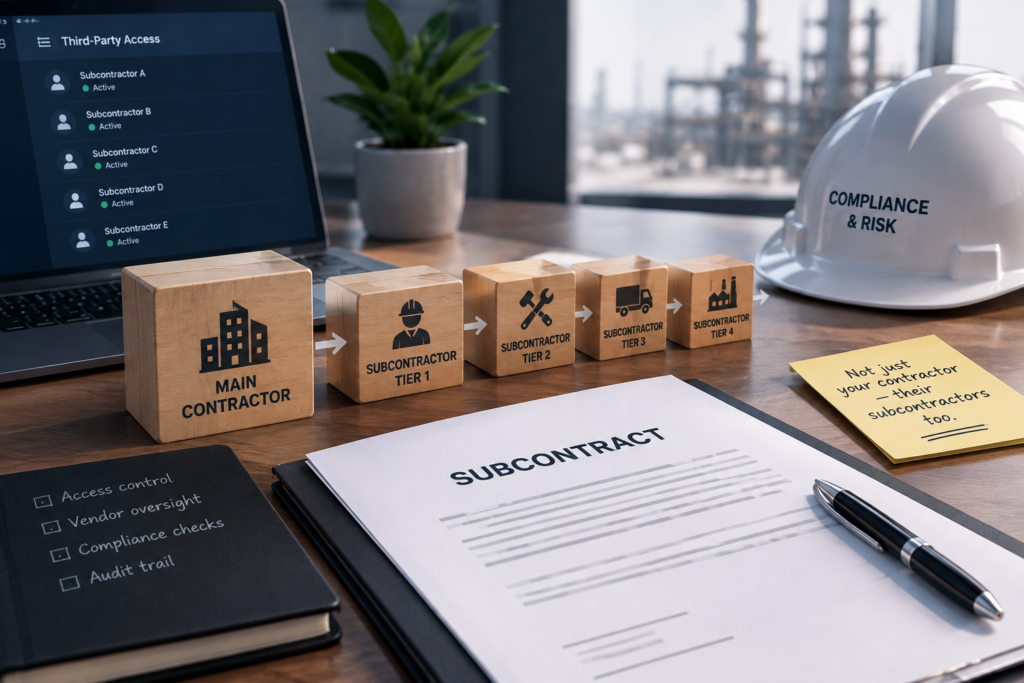
- IEC 62443-2-4 on the service provider – the systems integrator and maintenance contractor holding the standing remote access. This is the party NIS2 Article 21(2)(d) names alongside suppliers, and the one most capital project specifications omit entirely. Note also that the current edition is IEC 62443-2-4:2023, Edition 2.0; a spec still citing the 2015 edition is citing a superseded document.
To that, add the twelve asks in the CISA/NSA joint guide Secure by Demand: Priority Considerations for Operational Technology Owners and Operators when Selecting Digital Products (13 January 2025), co-sealed by twelve agencies including TSA, the European Commission’s DG CONNECT, BSI and NCSC-UK. Three of them are pure procurement leverage and are almost never priced: Ownership (full autonomy over maintenance and changes, minimising vendor dependency), Vulnerability Management (a clearly defined support period with patches supplied free of charge, and hardware and software bills of materials delivered with the product), and Upgrade and Patch Tooling (migration to a supported operating system version at no extra cost). The guide’s framing of the problem is the justification for treating this as a sourcing question at all: threat actors compromising OT “target specific OT products rather than specific organizations,” exploiting the same weaknesses across multiple victims.
One more timing trap. The CRA sets a support period floor of five years (Article 13(8)); recital 60 acknowledges that industrial control products are “often in use for significantly longer periods” and says manufacturers should ensure longer support – but the manufacturer sets the number, and the regulation gives the buyer no right to more. Equipment ordered in 2026 for a 2029 startup, with a declared five-year support period, is out of support in 2031 on a plant with twenty-five years to run. Fix the support period in the purchase specification at order placement and ask for the Annex VII technical documentation justifying it, because nothing downstream will fix it for you.
The two things nobody will supply later
Two closing findings are worth stating because they remove the fallback positions.
No mainstream EPC standard form contains a supplier cyber security clause. A site-wide search of FIDIC’s publications returns conference items and no clause, sub-clause, special provision or guidance note on cyber security. NEC4’s secondary options run X1 to X22 and X29 with no cyber option; X10 Information Modelling is a BIM and project-information clause, not an OT security one. Cyber obligations on OT vendors are therefore entirely bespoke drafting, living in employer’s requirements and technical specifications – which is to say, in documents procurement writes.
And the insurance fallback has narrowed. The Lloyd’s Market Association model cyber clauses map to the classes that carry capital projects: Engineering (risk codes CB, CC) to LMA5400 or LMA5401, and Energy Construction (risk code EC) to LMA5403 or LMA5402. The material change from the predecessor NMA2914/NMA2915 clauses is that the writeback for resulting fire or explosion has gone. A cyber-induced physical loss during commissioning or early operations may fall outside the construction all-risks programme entirely – and under the broader exclusion, even a non-malicious configuration error routed through a digital system can be caught.
That reframes the whole question. Supplier cyber assurance on a capital project is not a compliance line item to be closed out at handover. It is an uninsured-loss control that has to be bought at specification stage, evidenced per vendor, and – because support periods expire, certifications lapse, and the integrator who commissioned the plant is not the contractor who maintains it – maintained as live supplier data for the life of the asset. The record set NIS2 Article 21(3) demands, the recurring audit Saudi OTCC 4-1-1-4 demands, and the 15-month review cycle CIP-013 demands are the same record set. Keeping it current across a vendor population a project inherits at handover is a supplier lifecycle management problem, which is the discipline Dharas applies to it.
The alternative is the position 54% of operators are already in: finding out what the contract did not say, after the incident.